On October 29, 2026, approximately $6.3 billion in cryptocurrency began disappearing from wallets controlled by Binance, the world's largest cryptocurrency exchange. There were no masked robbers, no explosions, no getaway vehicles, and no physical vaults to breach. The theft unfolded through digital transactions that appeared on public blockchains, where anyone could eventually examine them but almost nobody could stop them. According to blockchain intelligence firm TRM Labs, most of the stolen value moved within approximately twenty minutes. The criminals had exploited financial infrastructure to make its own systems participate in one of the largest thefts in history.
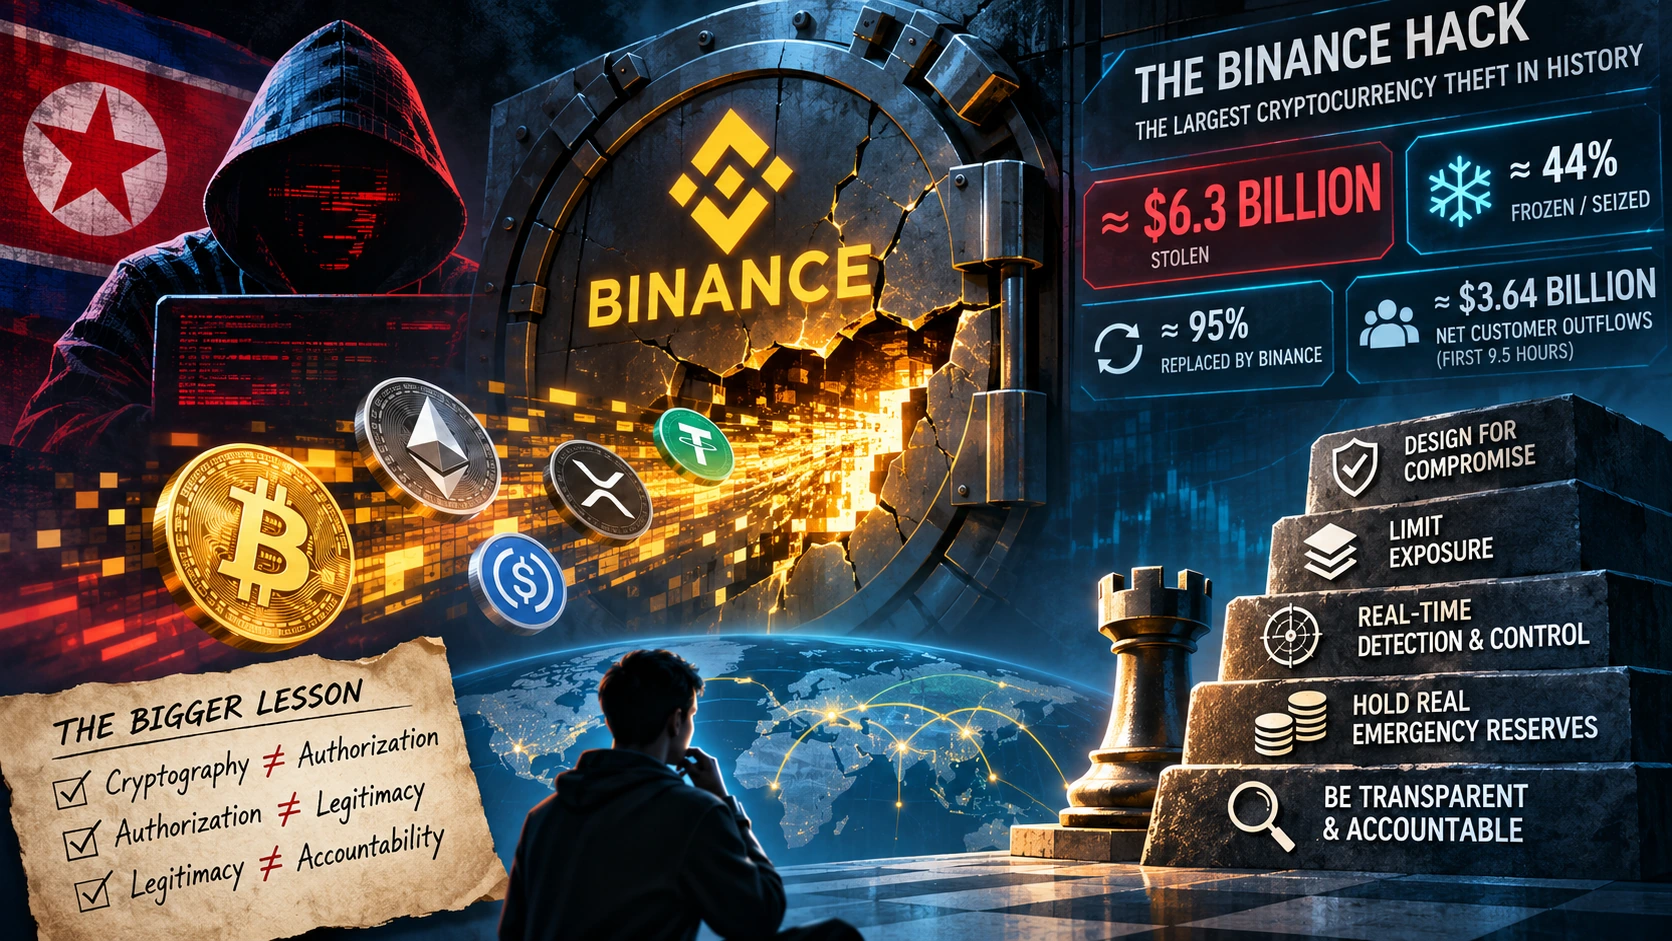
The scale was difficult to comprehend. Binance estimated the stolen assets at roughly $6.3 billion. TRM Labs calculated approximately $6.36 billion, while Elliptic estimated $6.43 billion, reflecting differences in tracing and valuation. Even the lowest estimate exceeded the approximately $1.46 billion stolen from Bybit in February 2025 by more than four times. For an industry accustomed to spectacular losses, this was an entirely different magnitude.
But the most disturbing aspect of the attack was not the amount stolen. It was what the theft revealed about the modern financial system. Cryptocurrency was supposed to make financial ownership more secure through mathematics, decentralization, and transparent verification. Yet billions remained vulnerable because the institutions handling that technology depended on permissions, computers, employees, and operational processes that could be compromised. The blockchain did not need to fail. The machinery of trust surrounding it was enough. And that distinction carries lessons far beyond cryptocurrency.
Twenty Minutes That Changed the Conversation
According to TRM Labs, the attack began at approximately 20:05 UTC, when Binance wallets on the XRP Ledger transferred large quantities of XRP to an address controlled by the attackers. Other blockchain networks followed in rapid succession, including Solana, Ethereum, Bitcoin, and Tron. At approximately 20:20 UTC, a Binance Bitcoin hot wallet transferred 18,270 BTC, worth roughly $1.47 billion at the time. Within minutes, enormous amounts of stablecoins and other digital assets were also leaving Binance-controlled wallets.
The attackers had apparently prepared their operation in advance. TRM investigators identified preliminary transactions, deployed code, and tests conducted before the main theft. This was not an impulsive criminal discovering an unlocked digital door. It appeared to be a coordinated operation in which access, timing, transaction execution, and the subsequent movement of stolen funds had been carefully considered.
The central activity occurred within a short window, although additional unauthorized transfers continued later that evening. Investigators identified activity across multiple blockchain networks. The diversity of affected assets mattered because it suggested the attackers were not simply exploiting an isolated vulnerability in one cryptocurrency. Something more consequential appeared to be happening within the infrastructure responsible for controlling Binance's wallets.
Binance suspended withdrawals, isolated compromised systems, revoked affected authorizations, and began investigating the source of the attack. These measures were necessary, but they came after a substantial portion of the losses had already occurred. This is one of the essential asymmetries of digital finance: a criminal may need only minutes to move billions, while investigators, engineers, regulators, and financial institutions may require months to determine exactly what happened and whether the money can be recovered.
The speed that makes cryptocurrency useful can also make a successful intrusion devastating.
How Can a Secure Blockchain Be Used to Steal Billions?
To understand the failure, distinguish three things that are often treated as interchangeable: a cryptographically valid transaction, a legitimately authorized transaction, and a financially responsible transaction. They are not the same.
Blockchains verify that transactions satisfy their technical rules. They do not possess an independent understanding of whether a transfer represents an ordinary customer withdrawal, a corporate treasury movement, or a theft initiated through compromised infrastructure. A valid digital signature can prove that the necessary cryptographic authority was exercised. It does not necessarily prove that the rightful decision-maker intended the transaction.
Centralized exchanges hold cryptocurrency on behalf of customers. Their wallets interact with operational systems that manage deposits, withdrawals, liquidity, security approvals, and transfers between accounts. Some wallets are maintained in highly restricted environments, commonly called cold storage. Others, known as hot wallets, remain connected to operational infrastructure to facilitate routine transactions.
Hot wallets are necessary for efficient exchange services, but their accessibility creates additional risk. Their security depends not only on private keys but also on the systems capable of requesting, authorizing, and executing transfers. The Binance incident demonstrated how dangerous those relationships can become when attackers gain access to the wrong part of the system.
The EIP-7702 connection
Blockchain researchers identified important activity involving Ethereum's EIP-7702 functionality, introduced in the May 2025 Pectra upgrade. EIP-7702 allows certain Ethereum accounts to delegate their execution behavior to smart-contract code. It was designed to improve wallet functionality and enable more sophisticated account features.
In the Binance attack, TRM Labs identified a transaction containing fifty prepared authorizations associated with a Binance hot wallet. These were intended to account for different transaction sequence numbers, known as nonces. One matched the wallet's state when the transaction executed, enabling delegation to code controlled by the attacker. According to the firm's analysis, the attacker used that delegated authority to transfer significant quantities of assets, including Ether and stablecoins, from the compromised wallet. The delegation also allowed additional arriving funds to be swept away.
This was not evidence that Ethereum's underlying cryptography had been broken or that EIP-7702 itself was inherently defective. Rather, the attackers appear to have obtained or induced authorization that should never have been available to them. Transactions on other affected blockchains were executed through ordinary signed transfers, suggesting a broader compromise of systems responsible for authorizing wallet activity.
Binance initially identified a potentially compromised development-and-operations engineer's laptop, later reporting additional points of breach. The company stated that it had found no evidence that wallet private keys had been leaked. That finding is important, but it does not conclusively establish the complete mechanism. A signing system can potentially be abused without the attacker extracting a private key into their own possession.
As of November 1, Binance had not published its complete post-incident technical investigation. The precise initial access method, the full chain of internal compromises, and the failures of specific approval controls remained subjects of investigation. The central lesson, however, was already visible: protecting the secret key is not sufficient if an attacker can manipulate the systems that are trusted to use it.
The North Korean Connection
On October 31, the Federal Bureau of Investigation publicly attributed the theft to North Korea's TraderTraitor operation, following similar assessments by blockchain intelligence companies. TraderTraitor has been associated with sophisticated attacks against cryptocurrency businesses, including the February 2025 Bybit breach. These operations illustrate how cybercrime has evolved from opportunistic theft into a potentially strategic activity conducted by well-resourced groups.
The allegation of North Korean responsibility carries consequences beyond Binance's balance sheet. U.S. authorities have repeatedly linked North Korean cryptocurrency thefts to efforts to obtain funds outside conventional international financial channels, including activity associated with prohibited weapons programs. North Korea has historically denied involvement in state-sponsored cybercrime. The exact motivations behind this particular attack cannot be established solely from the public attribution. Nevertheless, the incident demonstrates why cryptocurrency infrastructure has become attractive to sophisticated state-linked attackers.
Digital assets can move across international networks and through a complicated ecosystem of exchanges, decentralized protocols, bridges, and other intermediaries. Transactions may be visible on public ledgers, but tracing them is not equivalent to recovering the money or identifying the people operating the wallets.
The attackers also benefit from a striking imbalance of responsibility. A cryptocurrency exchange must protect its systems continuously. An adversary needs to identify only one sufficiently consequential weakness. When the adversary can invest substantial resources in planning, social engineering, malware development, and intelligence gathering, conventional corporate cybersecurity practices may prove inadequate.
This is no longer merely a problem of protecting financial websites from hackers. It is a problem of defending financial infrastructure against organized and potentially state-supported adversaries.
The Race to Freeze the Stolen Money
After the theft, an extraordinary effort began to prevent the attackers from converting and moving the stolen assets. Blockchain investigators traced suspicious transactions while cryptocurrency issuers, exchange operators, law enforcement agencies, and infrastructure providers worked to identify assets that could still be restricted.
Binance reported that approximately $3 billion had been frozen on-chain. Elliptic independently verified about $2.85 billion in frozen or seized assets in its November 1 analysis, representing approximately 44% of the total value it identified as stolen. Much of this intervention involved stablecoins, particularly USDT and USDC, whose issuers possess technical mechanisms to restrict designated token holdings. Other infrastructure participants also took action.
The figures are impressive, but they require careful interpretation. There are three different concepts in this recovery process: assets that have been located, assets that have been frozen or seized, and assets that have actually been returned to their rightful custodian. Locating money does not mean controlling it. Freezing money does not automatically mean recovering it. And replacing stolen assets from a company's treasury does not mean the original stolen assets have been retrieved.
For assets such as Bitcoin and Ether, the challenge is different. Their native blockchain transactions cannot generally be reversed or frozen by a central token issuer. Recovery may depend on identifying the individuals responsible, obtaining control over relevant private keys, or intercepting funds through cooperating intermediaries. For stablecoins, issuer-controlled restrictions can make immediate containment more achievable.
The result is a fascinating contradiction. Cryptocurrency was developed partly to reduce dependence on centralized financial authorities. Yet one of the most effective defenses following this theft was the ability of centralized organizations to intervene. Too little intervention may leave victims without practical remedies. Too much control may create opportunities for censorship, political interference, or arbitrary restrictions on legitimate owners. Future digital finance will need to navigate this dilemma rather than pretend it does not exist.
Binance's $6.3 Billion Response
Binance's immediate financial response was unusually consequential. The exchange announced that it would absorb the losses rather than pass them on to customers. By October 30, the company reported setting aside more than $6.34 billion to address the impact, with approximately $5 billion already held in the affected token assets. Binance subsequently described using a combination of corporate treasury resources, part of its Secure Asset Fund for Users (SAFU), and part of its futures insurance fund to replenish missing assets.
By November 1, Binance stated that it had replaced approximately 95% of the impacted assets. It also reported that balances for major tokens, including BTC, ETH, BNB, USDT, USDC, SOL, and XRP, were fully backed. The remaining portion largely involved less-liquid tokens that were more difficult to purchase in sufficient quantities. The company began restoring withdrawals in phases on November 1 after security checks, prioritizing heavily used networks and assets.
These actions were significant, but they did not eliminate every uncertainty. Binance's asset-backing figures were company-reported, and its new proof-of-reserves verification process was still being completed. A proof-of-reserves system can help customers evaluate whether reported holdings support customer balances, but it is not necessarily equivalent to a comprehensive independent financial audit covering all liabilities, ownership restrictions, operational risks, and corporate obligations.
Reopening withdrawals exposed another consequence of a major security failure: even customers whose balances have been replenished may question the safety of leaving their money with the institution. During the first nine and a half hours after withdrawals resumed, Binance reported approximately $4.65 billion in gross customer withdrawals and $1.01 billion in deposits, resulting in net outflows of around $3.64 billion. According to the exchange, that represented about 2.1% of its reported $171 billion in assets. Binance said activity began stabilizing after the initial surge.
Those figures reflect a substantial test of customer confidence. They do not, by themselves, establish that the exchange was insolvent or that customers would experience permanent losses. Still, the episode revealed something essential about modern finance: repairing an institution's balance sheet and repairing its reputation are different undertakings. Money may be replaced with treasury funds. Trust cannot be replenished by a simple accounting entry.
What the Hack Reveals About Cryptocurrency's Centralization Problem
Bitcoin was introduced with the possibility of transferring value without depending entirely on trusted financial intermediaries. Yet the growth of cryptocurrency has produced a curious outcome. Much of the industry's activity now occurs through large centralized exchanges holding enormous quantities of customer assets.
These institutions provide valuable services. They simplify trading, facilitate liquidity, support different digital assets, and make cryptocurrency accessible to people who might otherwise find self-custody intimidating or technically demanding. But their success has also created concentrations of operational authority.
The larger an exchange becomes, the more consequential its failures can be. A platform may employ sophisticated security personnel, advanced cryptographic infrastructure, complex monitoring systems, and substantial emergency reserves while still depending on a limited number of privileged systems capable of moving extraordinary amounts of money.
There is a difference between decentralizing the settlement network and decentralizing the power to authorize transactions. The Binance theft exposed that difference dramatically. Financial security cannot be measured solely by the strength of cryptographic protocols. Institutions are combinations of technology and human organization: employees, contractors, administrators, vendors, approvals, updates, emergency procedures, and business incentives.
Every connection between those elements creates a relationship of trust. Every relationship of trust must be examined for what could happen if it were abused. The solution is not to eliminate every intermediary; it is to prevent any single failure from becoming catastrophic.
Five Lessons for the Next Generation of Financial Security
1. Design systems around the possibility of compromise
The traditional security objective has often been to prevent attackers from entering protected systems. That remains essential, but it is insufficient. Financial institutions should assume that a privileged computer, employee credential, internal service, or vendor environment may eventually be compromised.
Critical systems should operate under carefully restricted permissions. Administrative access should not automatically provide authority over large financial transfers. Signing infrastructure should be isolated from ordinary development environments. Consequential transactions should require genuinely independent checks. The question should not be whether unauthorized access is possible. It should be how much damage an attacker could cause after obtaining it.
2. Put hard limits on the amount of money that can move
Exchanges need to process legitimate withdrawals efficiently. But this should not mean that enormous quantities of customer assets can be transferred through the same approval pathways used for ordinary transactions. Institutions should evaluate transaction ceilings, independent authorization for exceptional withdrawals, destination restrictions, and automatic controls that pause unusual activity.
A system processing thousands of ordinary withdrawals should distinguish distributed customer activity from a sudden concentration of value flowing toward unfamiliar addresses. A temporary interruption may be inconvenient. A catastrophic unauthorized transfer can threaten the institution itself.
3. Make monitoring capable of stopping transactions
A system that discovers suspicious behavior after billions have left may be useful to investigators, but it has failed as an immediate defensive barrier. Monitoring should connect to controls that can limit damage.
The Binance incident illustrates the importance of detecting coordinated activity across blockchains rather than treating each network as an isolated environment. Unusual authorization patterns, sudden changes in transaction volume, unexpected smart-contract delegations, and concentrated transfers should trigger escalating scrutiny. Not every unusual transaction is malicious, and overaggressive intervention can harm legitimate customers. But the largest financial movements should not be indistinguishable from routine automated activity.
4. Build emergency reserves that can withstand real crises
Binance's ability to commit substantial financial resources demonstrated the importance of emergency capital. But reserves must be more than reassuring labels. Institutions should demonstrate what assets they hold, whether those assets are genuinely available, how quickly they could be deployed, and what market conditions could reduce their usefulness.
Stress tests should examine cyberattacks combined with market volatility, customer withdrawals, and temporary loss of access to important services. A reserve that appears sufficient under ordinary conditions may become less effective when prices are falling and liquidity is disappearing. Independent examination of financial resilience should become a core expectation.
5. Treat transparency as an ongoing responsibility
The public needs more than declarations that money is safe. Following a major incident, a credible institution should explain what has been established, what remains unknown, which safeguards failed, what has been changed, and what independent evidence supports its financial claims.
Binance committed to publishing a detailed post-incident report. A useful report should examine the attacker's access, the affected authorization pathways, why suspicious transfers were not prevented earlier, and the controls introduced to prevent recurrence. The most valuable security disclosure does not simply announce that a problem has been fixed. It explains why the solution addresses the actual causes.
What Individual Investors Should Do Differently
For ordinary investors, the Binance hack presents a practical lesson about the difference between ownership and custody. Keeping cryptocurrency on an exchange may be convenient, particularly for frequent traders. But assets held through a custodial platform depend on that platform's security and operations. Even when an exchange promises to cover losses, withdrawal restrictions may temporarily prevent customers from accessing their holdings.
Investors should consider how much cryptocurrency they genuinely need to maintain on trading platforms and whether their long-term holdings would be better protected through alternative custody arrangements. Self-custody can reduce exposure to exchange failures, but it is not automatically safer for everyone. Hardware wallets, recovery phrases, transaction verification, and private-key management introduce responsibilities that some people may find difficult. A lost recovery phrase or a mistaken transaction can be just as devastating as an institutional breach.
For investors using centralized exchanges, strong authentication, withdrawal-address controls, device security, and skepticism toward unexpected messages are important defenses. Phishing-resistant security keys are worth considering where supported. Major hacks also create opportunities for scams: criminals may impersonate support employees, promise compensation, or persuade customers to disclose credentials and recovery phrases. Verify notifications by opening official platforms independently rather than following unfamiliar links.
There is also a broader lesson about diversification. Investors commonly diversify across different assets; they should also consider diversification of custodial risk. Owning several cryptocurrencies provides little protection against the failure of the one exchange holding all of them. The appropriate solution differs by individual, but the question deserves attention before an emergency occurs. The worst time to learn how custody works is when withdrawals have already been suspended.
Regulation After the Largest Crypto Theft
The Binance incident challenges the argument that financial regulation is simply an obstacle to technological innovation. Poorly designed rules can impose unnecessary costs, but institutions safeguarding enormous amounts of customer money create risks extending far beyond their shareholders. Customers need clarity about custody arrangements, the legal treatment of their assets, financial reserves, incident reporting, and the institution's ability to absorb unexpected losses.
Regulators should focus on those outcomes rather than transfer every traditional banking rule unchanged to every cryptocurrency business. Some principles are broadly applicable: customer assets deserve appropriate safeguards; critical operations must be resilient; major failures should be disclosed promptly and accurately; and financial contingency arrangements should withstand independent examination.
International cooperation is especially necessary because blockchain transactions can cross jurisdictions much faster than legal procedures. Efforts to freeze stolen funds demonstrate that coordinated action can matter, but they also reveal the limitations of a fragmented system in which one asset can be frozen through its issuer while another moves freely beyond immediate intervention.
The objective should not be to eliminate innovation through regulation. It should be to ensure that innovation does not require customers to assume risks they cannot reasonably evaluate. Financial freedom is not particularly meaningful when it depends on blindly trusting the institution holding your assets.
What Remains Unknown
Despite the detail available from public blockchains, fundamental questions remain unresolved. How did the attackers obtain access to Binance's transaction authorization infrastructure? Which internal controls were bypassed, and how? Why did the initial suspicious activity fail to prevent subsequent transfers? What architecture changes will permanently limit similar risks?
The eventual answers matter more than speculation about one vulnerable computer or software feature. It is also too early to determine how much stolen cryptocurrency will ultimately be returned. Frozen assets remain subject to further recovery procedures, while other funds may remain under attacker control or move through the cryptocurrency ecosystem.
Binance's commitment to cover customer losses is significant. Its long-term implications depend on completed asset replenishment, independent verification, and demonstrable changes to the weaknesses responsible for the attack. This remains an ongoing investigation, not a closed chapter. The first explanation after a major technological failure is rarely the complete explanation.
The Wisdom of a $6.3 Billion Mistake
There is something almost philosophical about the Binance hack. Human beings developed cryptocurrency partly because they were dissatisfied with systems requiring too much trust in institutions. Blockchain offered a different approach: transactions governed by transparent rules and verified through cryptography. But reducing the need for trust does not eliminate human judgment from the world around the technology.
Someone still decides how an exchange operates. Someone determines which systems possess financial authority. Someone approves software, manages infrastructure, reviews alarms, and decides when transactions should be stopped. Those decisions are not mathematical certainties. They are expressions of organizational judgment, and organizational judgment can be flawed.
The most dangerous form of technological confidence emerges when we confuse a sophisticated tool with an infallible system. Encryption can be strong while access controls are weak. Financial reserves can be substantial while operational safeguards are inadequate. A blockchain can operate flawlessly while billions are transferred to someone with no legitimate right to receive them.
The lesson extends beyond finance. Modern civilization depends on interconnected systems that operate faster than humans can meaningfully supervise them. Artificial intelligence, automated trading, cloud infrastructure, digital identity, healthcare networks, and critical utilities all face variations of the same challenge. As systems grow more powerful, the consequences of misplaced authority grow with them.
The response cannot simply be to demand smarter employees or more expensive technology. People make mistakes. Software contains weaknesses. Sophisticated adversaries search for opportunities. Resilient systems must be built with those realities in mind. A truly secure institution is not one that promises nothing will ever go wrong. It is one designed so that a failure does not automatically become a catastrophe.
Binance's response may ultimately protect its customers from direct financial losses. The company's recovery efforts deserve to be evaluated fairly. But replacing stolen assets does not resolve the more fundamental question of why so much value could be placed at risk so quickly.
The enduring significance of October 29 will not be measured only by dollars stolen, funds frozen, or arrests made. It will be measured by whether the financial industry learns to distinguish the appearance of security from genuine resilience.
The future of money does not need to abandon cryptography, decentralization, or innovation. It needs to recognize their limits and design surrounding institutions accordingly. Because technology may change how humanity stores and transfers wealth, but it does not change the oldest weakness in financial history: the tendency to place too much confidence in systems whose vulnerabilities remain poorly understood.
The real lesson of the Binance hack is simple: trust should never be unlimited, authority should never be unchecked, and no single failure should be allowed to threaten everything.
That is not merely a principle for cryptocurrency. It is a principle for the digital world we are building.
Sources and reporting
The account above reflects reporting and announcements available through November 1, 2026. Attack-mechanism conclusions remain provisional pending completion of Binance's technical investigation. Frozen assets and customer assets replaced from Binance's funds are distinct.